

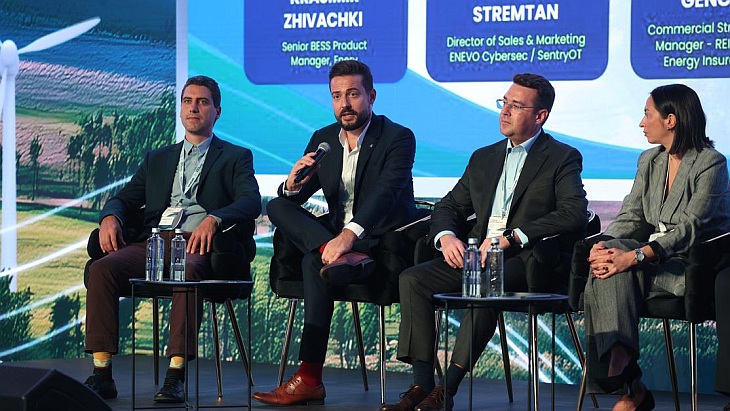
Cybersecurity obligations in energy should not be treated as a separate compliance exercise. Operators need people, processes and technical capabilities that allow them to detect an incident, understand its effect on operational systems and act before a cyber event becomes a prolonged disruption of the physical process, said Mircea Stremțan, Sales & Marketing Director at ENEVO Cybersec / SentryOT, during the launch conference for the Code of Good Practice in Renewables, 2026 edition, organised by RWEA and RPIA.
The growing regulatory burden, including NIS2 requirements, adds complexity, but the practical challenge is to translate rules into working capabilities. “We have developed SentryOT, an energy-focused cybersecurity platform that operationalises NIS2 requirements into concrete, day-to-day security capabilities such as OT visibility, early incident detection, regulatory reporting and coordination of incident response teams,” Stremțan said.
From a cyber alert to operational impact
For an energy operator, detecting suspicious activity is only the beginning. The next task is to establish where the event has propagated, which IT and OT systems were affected and whether the behaviour of the infrastructure has changed. In an OT environment, the relevant consequence is not simply an alert, but whether configurations, commands, equipment or the physical process itself have been affected.
The response has to build a common cyber-operational picture. Cybersecurity specialists need to understand the compromise and preserve evidence; networking teams need to contain the attack by isolating segments and blocking lateral movement paths; OT engineers need to determine whether safety-critical functions have been impacted or the process has been compromised.
The recommended sequence is practical: detect and contextualise the event, assess its operational impact, bring the relevant teams together, isolate affected elements where necessary, investigate what happened and restore critical functions in the right order. Documentation and reporting form part of the same process rather than a separate compliance-only exercise.
Technology, processes and people
Stremțan linked technical response directly to compliance, arguing that the two have to be managed together. Operators need to deal with the technical complexity of their infrastructure while also demonstrating that regulatory requirements are being met. The appropriate solution therefore depends on what the organisation operates, what risks it faces and what capabilities it already has, rather than on applying the same cybersecurity package to every asset.
The same logic applies before an incident. Visibility over operational assets, continuous monitoring and the ability to recognise abnormal cyber and operational behaviour shorten the distance between an initial signal and an informed decision.
For critical energy infrastructure, cyber resilience is ultimately tested after something goes wrong: whether the operator can understand the incident quickly, coordinate the right specialists, limit its propagation and restore the physical process safely. Compliance sets the requirements; operational readiness determines whether they work when they are actually needed.
The Code of Good Practice in Renewables is an initiative of RWEA and RPIA. The third edition, produced in 2026 with the involvement of Energynomics, benefited from the contribution of partners AI Clearing, Alerion, CMS, DLA Piper, Enercon, Enery, ENEVO Group, Eximprod, GE Vernova, Monsson, Nordex, Nyerges and Partners, OX2, Parapet, Raiffeisen, REIB, Scatec, TDP, Vestas and Waldevar. The Code was launched on October 1 at a conference held in Bucharest and is available free of charge, including in electronic format.