Ioana Manea, Chief Innovation Officer, Arctic Stream și Director General, Cyber Arena
In Romania, 91 per cent of employees say their organization has security measures in place, but on average they identify only 4.2 out of 10 of the solutions implemented, according to Ioana Manea, Chief Innovation Offi cer at Arctic Stream and Managing Director of Cyber Arena. In critical sectors such as energy and banking, investment must focus particularly on resilience. “I expect investment to focus increasingly on infrastructure segmentation, access control, AI and cloud security, monitoring and incident response,” Ioana Manea tells Energynomics.
What are the latest trends in cybersecurity investments, globally and in Romania?
Globally, we are witnessing a sustained increase in technology investments, and cybersecurity is becoming an increasingly important component of this eff ort. According to Gartner, global IT spending will reach $6.37 trillion in 2026, 14.2% above the 2025 level, with growth fueled mainly by investments in infrastructure for AI, cloud and software. Recently, a group of 100 global technology companies signed an open letter to ask world governments to invest more in cyber defense capabilities, as attacks based on artifi cial intelligence become more sophisticated and widespread. A large part of the budgets from the European Commission are directed towards projects involving cybersecurity and we observe an increased competitiveness in attracting such funds. In Romania, however, I believe that the discussion must be less about how much we spend and more about how we spend. In this sense, the Cyber Literacy Audit 2026, the most complex study that measures the level of knowledge, behaviors and security refl exes of employees and managers in their daily digital activity, conducted by MKOR for Arctic Stream and Cyber Arena, revealed important data.
Thus, according to the study, there is a significant gap between formal security and operational reality: 91% of employees declare that the organization has security measures, but they identify, on average, only 4.2 out of 10 implemented measures. VPN and MFA are recognized as active by less than half of the respondents.
In critical sectors such as energy, banking or utilities, the pressure for investment is even greater, as an incident can affect not only data, but also the continuity of essential services. In addition, European regulatory requirements, including NIS2, CRA, DORA, push organizations towards a more mature approach to risk management, continuity and incident response.
For the coming years, I expect investments to focus increasingly on resilience: infrastructure segmentation, identity and access control, securing AI and cloud, monitoring and incident response, but also training people. Because an organization does not become more secure just by acquiring technology. It becomes more resilient when technology, processes and people work together.
What were the main challenges of 2026 in terms of cybersecurity threats? What were the response vectors?
During 2026, we found that ransomware maintains its position as a recurring threat, but with increased virulence, systematically targeting public institutions and the pillars of critical infrastructure. In the domestic landscape, these attacks hit both the public and private sectors, validating a scenario in which criminal groups aim to destabilize vital organizations, where blocking activity generates operational and social consequences of major gravity. In Romania, however, the Cyber Literacy Audit shows that the “front door” remains, in many situations, an extremely familiar one: email. It is identified as the easiest access route, and phishing represents the most frequent threat encountered by employees. About eight out of ten incidents reported in the last 12 months involved suspicious emails or messages. Moreover, only 43% say they report suspicious emails to IT. Here we have a very interesting paradox: people may perceive the risk, but that does not automatically mean they follow the protocol. And the problem becomes even more serious when we talk about managers. They are more aware of the risk, but they adopt more risky behaviors: 31% use public Wi-Fi without a VPN, 33% enter internal documents into AI tools, and 43% frequently install unauthorized software on their work laptop. The response vectors must therefore be combined. We need technology, but also segmentation, visibility and traceability, incident response services and, above all, people trained to react correctly. In the event of an incident, the study shows that employees say they know what to do in the first 30 minutes – the average score is 5.8 out of 7 – but actually perform only 2.6 actions out of 10 possible to limit the risk. Here the difference between “I know” and “I know how to do” is very clear.
How has the appetite and openness of managers towards such services evolved, globally, in recent times? But in Romania?
I think the reluctance has reduced, but not disappeared. And it is natural: cybersecurity has moved from the “it would be nice to have” area to the “we must be able to demonstrate that we are protected and that we can continue to operate in the event of an incident”. Especially for essential and important organizations, the regulatory framework has accelerated this change. NIS2 has also shifted the discussion to management responsibility, business continuity, risk management and incident reporting.
But the Cyber Literacy Audit shows us that there is still a long way to go. 94% of managers say that their organizations have preventive measures in place, but almost half of organizations operate more reactively. Moreover, the human factor and budget constraints are perceived as the main strategic obstacles: 13% of managers indicate a lack of risk awareness, and 12% budget constraints.
I would say, therefore, that managers have become more open, but the investment must be translated into business language: what risk do we reduce, what process do we protect, how quickly do we detect an incident, how quickly can we recover and what nancial and operational impact do we avoid. In this sense, cybersecurity is no longer a “non-core” investment. It becomes a condition for business continuity. A positive sign is that 84% of managers say they have clear priorities, which include (1) training and awareness of employees (51%); (2) updating / purchasing technology and security systems (31%); respectively (3) improving access and security policies (29%). In the medium and long term, I expect that the diff erence will no longer be made by companies that “have cybersecurity”, but by those that constantly practice and measure it. This means testing, simulations, incident response exercises and continuous updating of people and processes. What should line managers (CIOs/CTOs) in Romania consider in the coming period? First of all, they should stop treating cybersecurity as an exclusive problem of the IT department: three quarters of employees with digital exposure, in Romanian companies, have an insuffi cient level of cyber literacy, and only 4% fall into the Cyber-Resilient category. Second, the CIO or CTO must view the infrastructure as an integrated system. Nearly half of employees work in a hybrid mode, combining personal and work devices and accounts. In this segment, 69% transfer documents through personal applications, 48% connect personal storage to the company computer, and reporting to IT is reduced. Third, the use of AI must be secured. It is not enough to give employees access to new tools; we must know what data they can enter, what data they cannot enter, where it goes, and what controls are in place. The study shows that managers enter internal documents into AI tools at a higher rate than do front-line employees. Finally, investing in exercises should not be ignored. Only 34% of employees have participated in practical attack simulations, and only 2% of mandatory training has an exclusively practical format. You cannot build resilience just by presenting and policies that employees sign off on as “Aware”. People need to practice making decisions under pressure, just like in Cyber Arena scenarios. In a real incident, the speed and quality of the decision can make all the diff erence.
What should we do to avoid a potential power blackout caused by cyberattacks?
What was considered the subject of a movie a year ago (Zero Day), unfortunately seems to be getting closer to reality in recent months. A recent example of an attack on such an energy infrastructure is the one in Poland, at the end of last year, with multiple attempted attacks on individual energy generation sources – solar parks and even individual wind turbines.
In the case of energy infrastructures, I would start from a simple principle: we must assume that an incident can occur and design the system so that an attack cannot simultaneously compromise all critical levels.
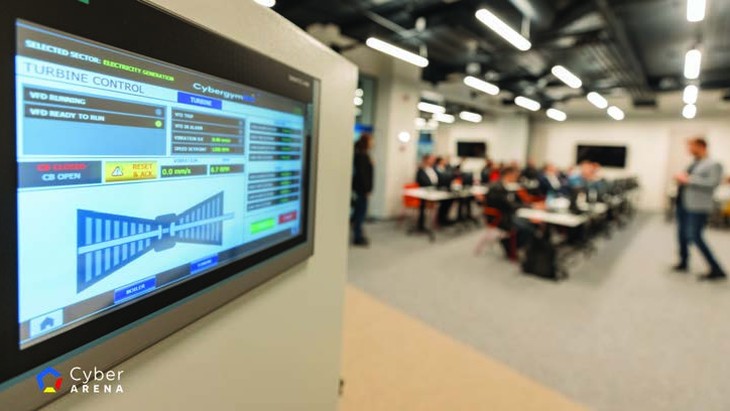
A first element is network segmentation. In industrial infrastructures, process networks – including SCADA – must be logically isolated from administrative networks, so that an incident starting in the user area cannot reach the area that controls production. Segmentation must also be thought out at the user and application level, to reduce the attack surface.
The second element is visibility. We need to know who, how and when connected, what happened and where an incident is propagating. Logs, monitoring and correlation of events allow for rapid detection, assessment of the amplitude of the attack, isolation of affected systems and efficient response.
The third is responsiveness and continuity. A critical infrastructure operator cannot afford to have the response plan written and forgotten in a drawer. It must be tested periodically, including through exercises involving both technical teams and management.
And here we return to the fundamental conclusion of the Cyber Literacy Audit: technology alone is not enough. 74% of Romanian employees with digital exposure have an insufficient level of cyber literacy, and only 22% of organizations are in the “Proactive & Optimized” category. In energy infrastructure, this means that resilience must be built on three levels simultaneously: technology, processes and people.
If we want to reduce the risk of a blackout caused by a cyber-attack, it is not enough to build a higher wall. We must ensure that if an attacker gets past the first wall, they cannot reach the entire system, that we can detect them quickly, that we can isolate the affected area and that people know exactly what they have to do to maintain or restore critical services.
_____________________________________________
The interview also appeared in the print edition of Energynomics Magazine, Q3 2026 issue.
In order to receive the printed or electronic issue of Energynomics Magazine, we encourage you to write us at office [at] energynomics.ro to include you in our distribution list. All previous editions are available HERE.